
Create an organization-owned automation identity
Use a service account for automation that must continue after its creator leaves. Management requires a GitHub organization owner with operational access and recent ownership verification.
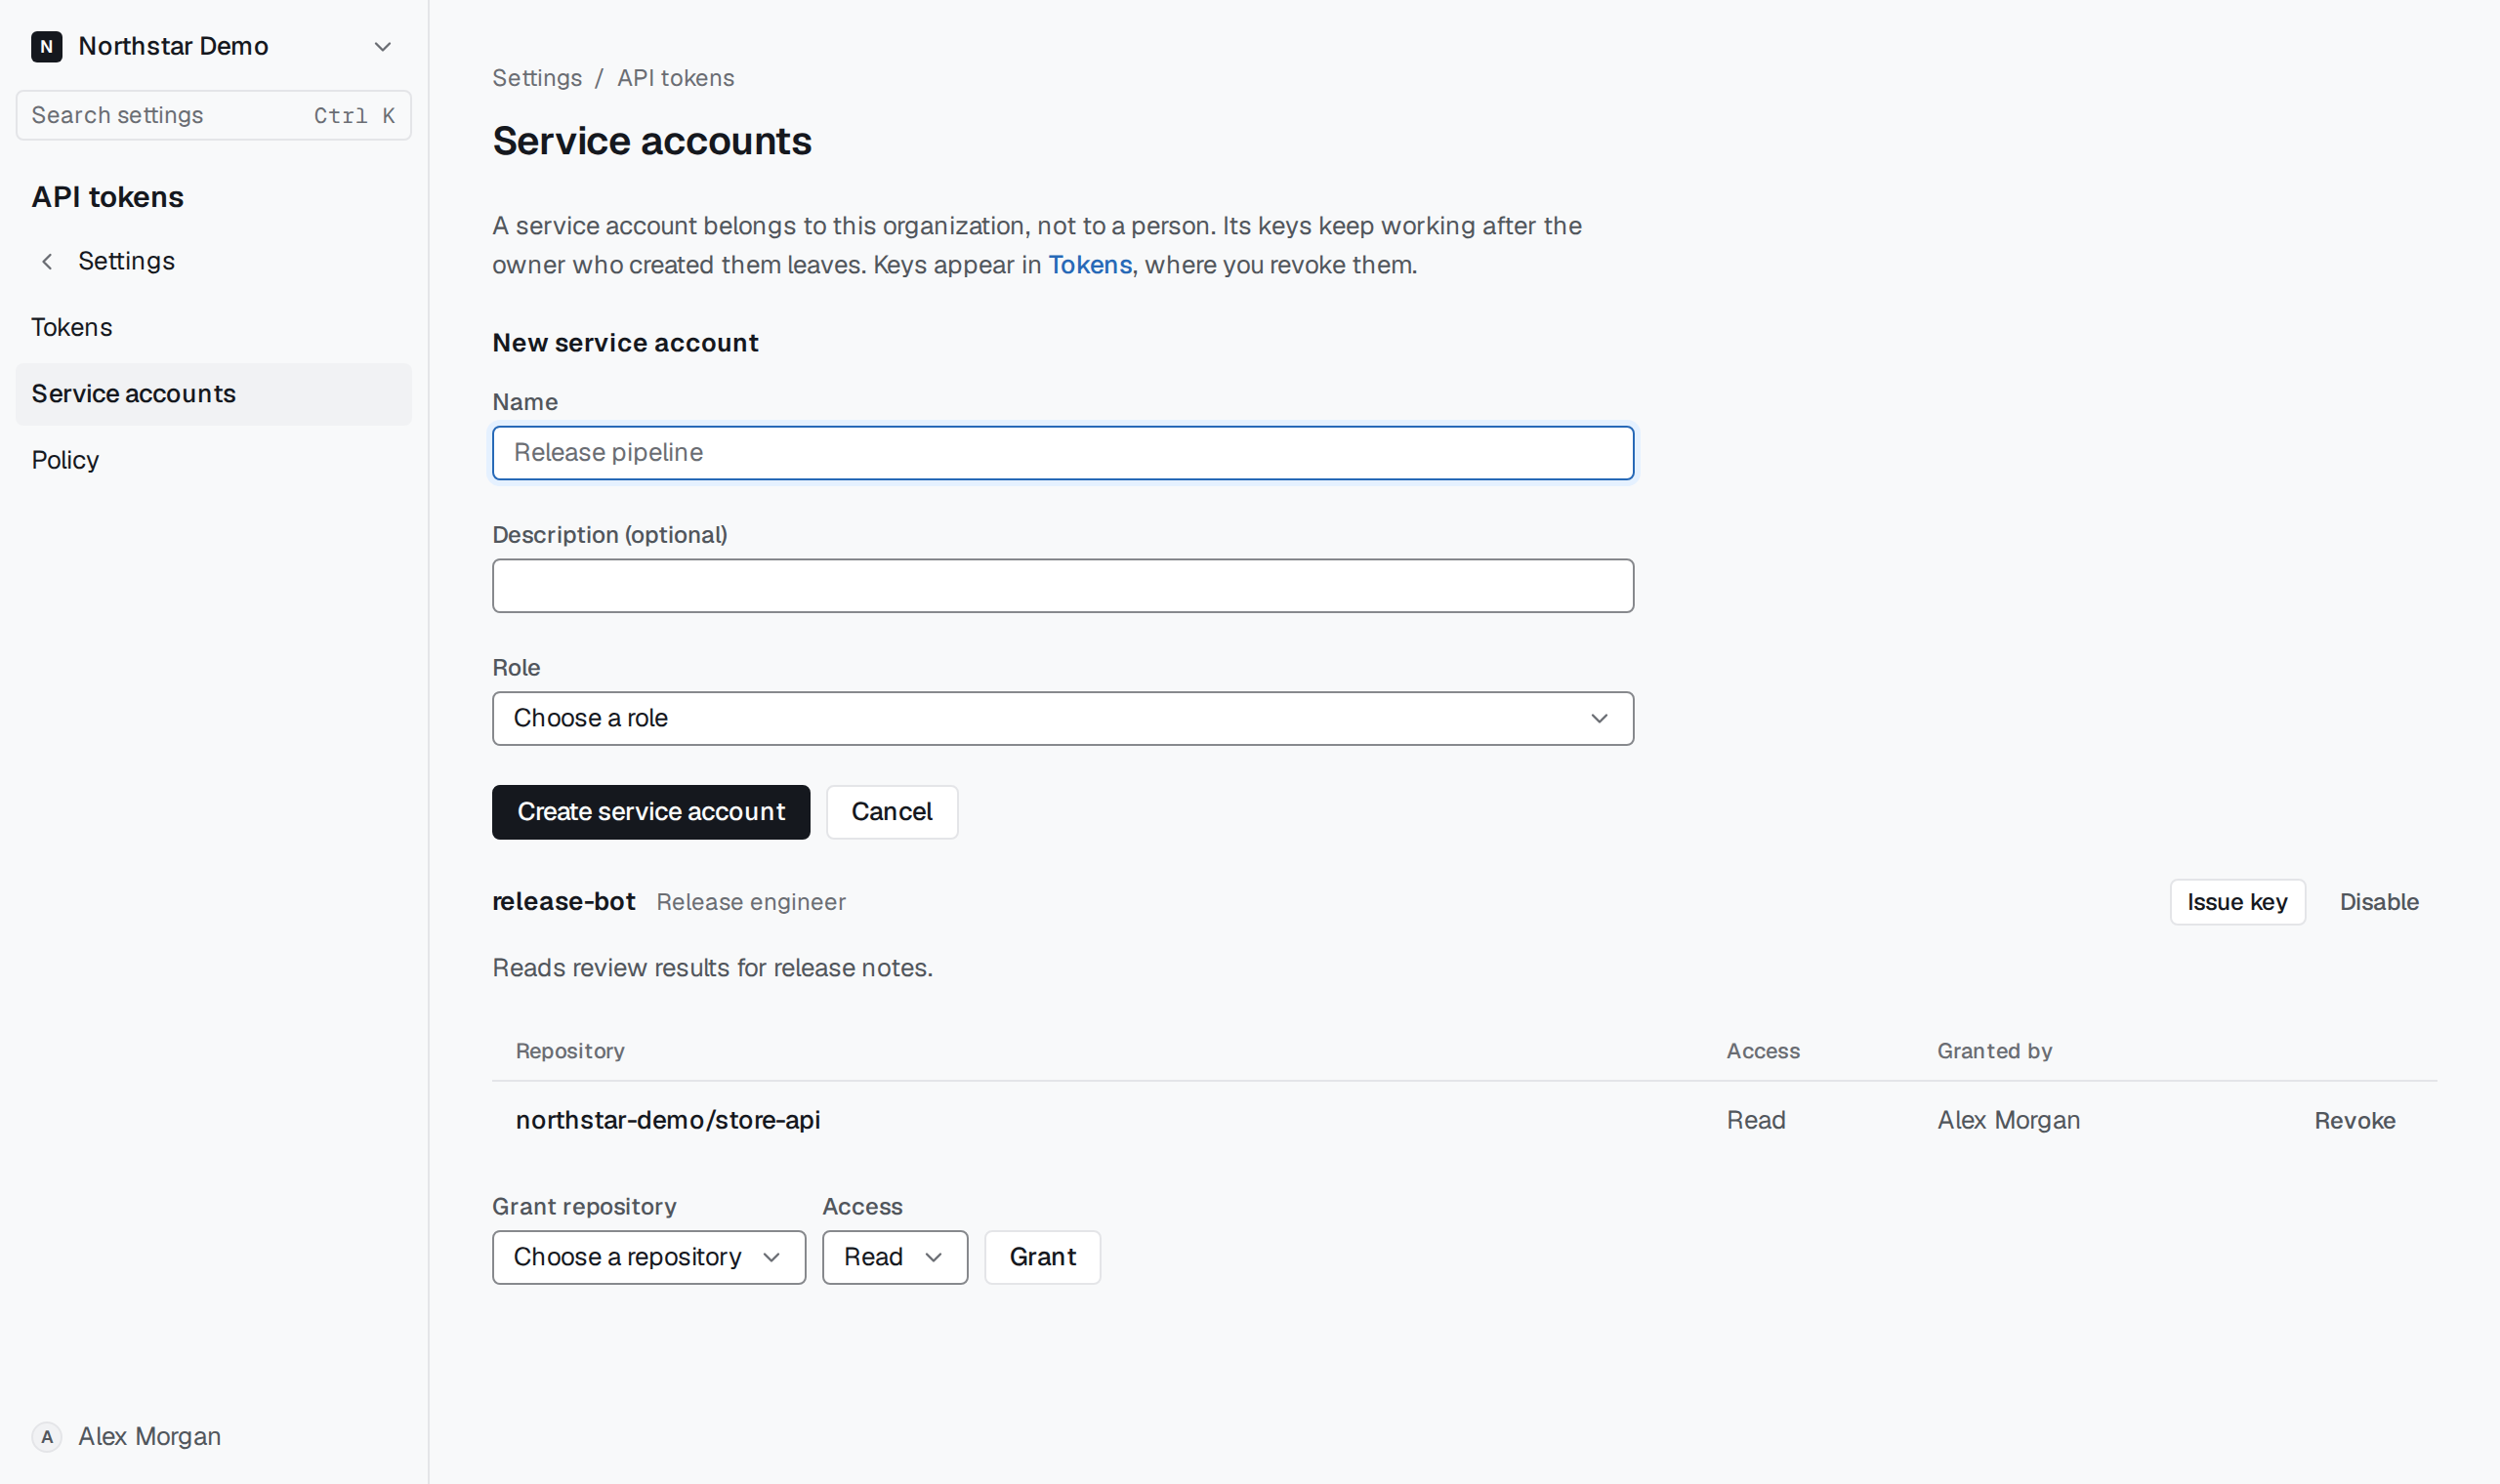
Choose the account role#
Open Settings → API tokens → Service accounts, select Create service account, and enter its name, optional description and role. A role that manages cloud trust or roles cannot be used. If none is available, first create an appropriate custom organization role.
Save the account, then grant the repositories it needs before issuing a key. A newly created account with no repository grants reads no repositories.